


Is Adware Malware? Understanding the Key Differences
Learn whether adware is malware, how they differ, and why adware poses security risks. Comprehensive guide to protecting your devices from unwanted software.
8 min read
Adware is software that automatically displays advertisements on your device to generate revenue for its developer.
Adware is software that automatically displays advertisements on your device to generate revenue for its developer. The term combines “advertising” and “software.” It ranges from legitimate, consent-based ad-supported applications to aggressive, malicious programs that install without permission, degrade performance, and compromise privacy.
Adware — short for advertising-supported software — is any program that serves advertisements to a user, typically through a web browser, desktop pop-ups, or within other applications. The defining characteristic is intent: adware exists to make money for its developer by putting ads in front of you.
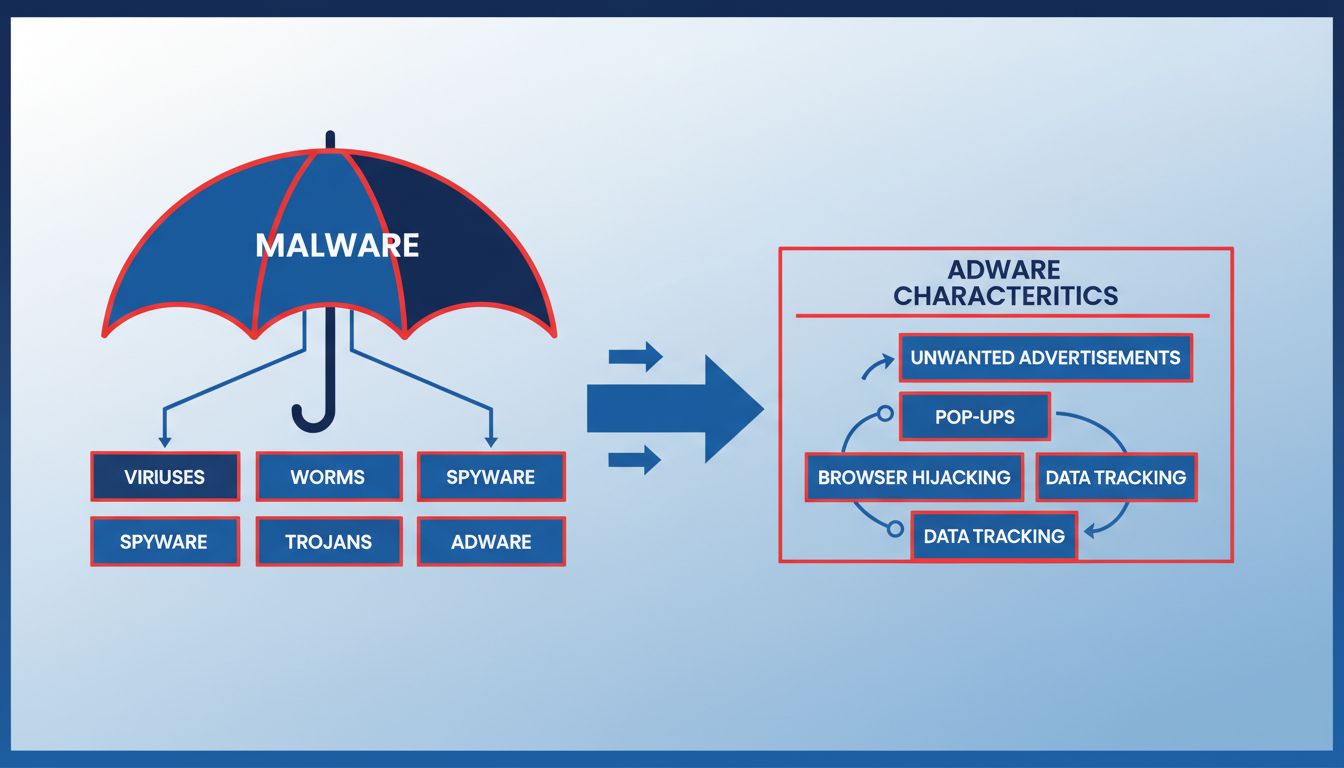
The Cybersecurity and Infrastructure Security Agency (CISA) classifies adware under the broader umbrella of unwanted software that can “display unwanted advertisements” and “track your browsing activity.” Security companies draw a line between two main categories:
Some adware goes further. It redirects your browser, changes your default search engine, injects ads into legitimate websites, and collects your browsing history to build a profile for targeted advertising. At that point, it crosses firmly into the category most security professionals call malware.

Set up advanced tracking in minutes. No credit card required.
Adware operates on a straightforward economic model: it installs itself on as many devices as possible, displays ads, and collects revenue each time those ads are viewed or clicked. Understanding that model is key to understanding why adware persists despite decades of detection tools.
Adware developers and the vendors who distribute it monetize through three channels:
| Model | How It Works | Typical Payout |
|---|---|---|
| Pay-per-click (PPC) | Revenue each time a user clicks an ad | — |
| Pay-per-view (PPV) | Revenue each time an ad is displayed (impression) | — |
| Pay-per-install (PPI) | Revenue each time bundled adware is installed on a device | — |
Larger, reputable ad networks employ fraud detection that blocks most adware traffic. As a result, adware operators frequently use smaller, obscure ad platforms with looser policies — which is why adware-delivered ads often feature low-quality or deceptive content: fake alerts, diet pills, get-rich-quick schemes, and adult material.
Beyond displaying ads, many adware programs collect data about you. They track:
This data serves two purposes. First, it enables targeted advertising — showing you ads you’re more likely to click, which increases the developer’s PPC and PPV revenue. Second, the data itself can be sold to third-party brokers, creating a secondary revenue stream. In some cases, the collected information feeds into phishing campaigns or identity fraud.
Adware is not a monolith. Security researchers and antivirus vendors group it by behavior, consent, and risk level.
Some adware programs are installed with full user knowledge and consent. Developers offer software for free and offset costs through in-app advertising. Examples include:
Legitimate adware discloses its advertising model in the terms of service. It does not hide its presence, does not change browser settings without permission, and provides a paid ad-free option or a clear opt-out. It is legal and, for many users, a fair trade.
PUPs occupy a grey zone. They may be mentioned somewhere in an installer — but the disclosure is buried, pre-checked by default, or written in confusing language. Users often install PUPs without realizing it.
Common PUP behaviors include:
PUPs are not always overtly malicious, but they degrade performance, clutter the browsing experience, and erode user control. Most antivirus software now flags PUPs during scans and offers to remove them.
At the far end of the spectrum, malicious adware installs without any consent, hides from the user, and actively harms the device. It may:
Malicious adware is unambiguously illegal in most jurisdictions and is treated as malware by all major security vendors.
Be the first to know about new features and product updates.
Adware reaches devices through several infection vectors, most of which exploit common user behaviors.
The most frequent delivery method is bundling. Adware is packaged inside the installer of a legitimate free program — often freeware or shareware downloaded from third-party sites. The adware component is pre-selected in the installation wizard, sometimes hidden behind “Advanced” or “Custom” installation options that users skip.
Once you click through a standard install, the bundled adware installs itself alongside the program you wanted — and you may never know it happened.
Some adware programs don’t wait for you to download anything. They exploit known vulnerabilities in your browser, operating system, or browser plugins to force an install. Visiting a compromised or malicious website is enough. This method — often called a drive-by download — works especially well on unpatched systems.
Attackers also distribute adware through fake update prompts. You might see a pop-up claiming that your browser, Flash Player (now obsolete, but still mimicked), or a media codec needs updating. Clicking the prompt installs adware instead.
Malvertising — injecting malicious code into legitimate ad networks — is another vector. A clean website can serve an infected ad that redirects to an adware installer, all without the site owner’s knowledge.
Adware doesn’t always announce itself. Some variants are subtle. However, several signs reliably indicate an infection.
One or two of these symptoms may indicate adware; several together make it highly likely. Windows users tend to encounter more adware variants simply because of the platform’s larger market share, but Mac adware has risen sharply in recent years — particularly browser hijackers and bundled PUPs.
Mobile devices — especially Android phones — are increasingly targeted. Signs include:
iOS adware is rarer due to Apple’s app review process, but it does appear through sideloaded apps, configuration profiles, and compromised enterprise certificates.
These terms overlap but are not interchangeable:
| Term | Definition | Relationship to Adware |
|---|---|---|
| Malware | Any software designed to harm, exploit, or compromise a device or its data | Malicious adware is a subset of malware |
| Virus | Malware that replicates itself by infecting other files | Adware does not self-replicate; it is not a virus |
| Spyware | Software that secretly monitors and collects user data | Many adware programs include spyware functionality |
| PUP/PUA | Software users may not want, but that isn’t outright malicious | Most adware falls into this category |
Adware is not a virus — it doesn’t self-replicate or corrupt files. But when it installs without consent, tracks behavior, and redirects traffic, it qualifies as malware. When it collects browsing history and personal data, it overlaps with spyware. Security companies frequently classify aggressive adware under all three labels.
The legality of adware depends on consent and jurisdiction. The key factors are:
Legitimate adware with clear disclosure and opt-in consent is legal. Malicious adware that hides its presence and collects data without permission is illegal under laws including the Computer Fraud and Abuse Act (CFAA) and various state consumer protection statutes.
Removing adware requires a methodical approach. Relying on a single step often leaves remnants that reinstall themselves.
C:\Windows\System32\drivers\etc\hosts to redirect traffic. Open it in Notepad as an administrator and remove any suspicious entries below the default localhost lines.If adware persists across removal attempts, a factory reset — followed by restoring data selectively from a clean backup — is the most reliable option.
Prevention is more effective than removal. The following practices reduce your risk to near zero.
Stick to the Microsoft Store, Mac App Store, Google Play, or the developer’s official website. Third-party download portals are the single largest vector for bundled adware. If you must download from a third-party site, choose “Custom” or “Advanced” installation and manually deselect every optional offer.
Most bundled adware relies on users clicking “Next” without reading. Slow down. Look for pre-checked boxes offering “additional software,” “recommended offers,” or “enhanced search.” Decline them all.
Operating system updates and browser patches close the vulnerabilities that drive-by downloads exploit. Enable automatic updates on Windows, macOS, Chrome, and Firefox.
A browser-based ad blocker like uBlock Origin stops many malvertising campaigns before they can redirect you. It also reduces exposure to deceptive ads that mimic system warnings.
Modern antivirus tools detect PUPs and adware — not just viruses. Windows Defender (built into Windows 10 and 11) includes PUP detection, though it must be enabled manually in some configurations. Third-party tools from Malwarebytes, Bitdefender, and Kaspersky offer more aggressive default detection.
Adware is a persistent threat to the affiliate marketing ecosystem because it can steal commissions and corrupt attribution data.
There are three common methods:
Cookie stuffing. Adware drops an affiliate tracking cookie on the user’s browser without the user actually clicking an affiliate link. When the user later visits the advertiser’s site and makes a purchase, the adware operator — not the legitimate publisher — gets the commission.
Link replacement. Adware detects when a user visits a merchant site and redirects the URL to include the adware operator’s affiliate ID. The original referrer loses credit for the sale.
Search injection. Adware modifies search results to route traffic through affiliate links. A user who types a merchant’s name directly into the address bar may still end up on a page tagged with the adware operator’s tracking code.
| Role | Impact of Adware |
|---|---|
| Advertisers | Pay commissions on sales that would have happened anyway. Skewed attribution data makes campaign optimization unreliable. |
| Publishers | Lose legitimate commissions when adware overwrites their cookies or redirects their referrals. Revenue drops without explanation. |
| Affiliate Program Managers | Face inflated, low-quality traffic in reports. Must invest time in fraud detection and chargeback processing. Program reputation suffers when publishers blame the network for stolen commissions. |
Adware-driven affiliate fraud is a form of malicious activity that damages every party in the ecosystem except the fraudster. Legitimate affiliate marketing — where publishers earn commissions by genuinely recommending products — has no connection to adware practices. The distinction matters: adware operators are not affiliates; they are fraudsters exploiting affiliate infrastructure.
Learn how to identify, remove, and prevent adware to keep your devices and data secure.
Learn whether adware is malware, how they differ, and why adware poses security risks. Comprehensive guide to protecting your devices from unwanted software.
Learn how adware harms your PC, including performance degradation, privacy risks, and security vulnerabilities. Discover detection methods and removal strategie...
An advertiser is a company or person who pays to place ads promoting products, services, or brands.
Join our community of happy clients and provide excellent customer support with Post Affiliate Pro.


Cookie Consent
We use cookies to enhance your browsing experience and analyze our traffic. See our privacy policy.